SASE Implementation: A Rollout Guide for Multi-Site IT Teams
If your team already understands Secure Access Service Edge (SASE) conceptually and you're past debating whether to adopt it, this SASE implementation guide is built for you. Rolling SASE out across more than one site looks different than it does on a whiteboard, and the real gap for most IT teams isn't the architecture. It's knowing what order to do things in.
We won't redefine SASE or walk through the SD-WAN and security service edge halves again here. If you're past the fundamentals and ready to plan the actual rollout, here's where to start: what trigger to look for, what to inventory before you touch any gear, how to pilot without disrupting the whole company, and how to sequence the work on a Cisco-based stack.
Start With the Problem You're Actually Solving
Before you touch any gear, name the specific problem driving this project. Skip the generic “define your business goals” advice you'll find everywhere else. A SASE implementation sticks when it's tied to a real, recognizable trigger, not an abstract mandate from three quarters ago.
- Too many standing VPN connections: Remote and branch users are creating security gaps a single perimeter can't cover anymore.
- A lease or contract renewal is coming up: An expiring SD-WAN or firewall contract is a natural, low-disruption point to fold in a SASE approach.
- New site opening: Adding a location is the easiest place to pilot a new architecture, since there's no legacy setup to migrate away from.
Take Stock of What's Already in Place
Once you know the problem you're solving, the next step is an honest inventory. This is about the practical constraints that decide how your rollout gets sequenced: what's expiring, what's aging out, and how much hands-on time your team actually has. If your existing network already runs on Meraki gear, it's worth understanding how Cisco's ownership has shaped licensing and support over time before you build your SASE deployment plan around it.
- Contract and renewal dates: Note when existing SD-WAN, firewall, and VPN contracts expire; these are natural transition points.
- Hardware age and support status: Flag anything nearing end-of-sale or end-of-life that would need replacing regardless.
- Team bandwidth: Be honest about how much hands-on time your team (or a partner) can realistically give this over the rollout window.
Pick a Pilot Site, Not the Whole Company
A single-site pilot is the fastest way to catch problems before they scale to your whole network. Resist the pressure to roll a SASE implementation out everywhere at once, even if leadership wants to see it live company-wide by next quarter. A pilot buys you room to fix mistakes quietly instead of publicly, and it's the fastest route to a SASE deployment that actually holds up under real traffic.
- Pick a representative site: Choose a location with typical user count and traffic patterns, not your smallest or most unusual site.
- Set a fixed pilot window: Give the pilot a defined start and end date so it doesn't quietly become permanent without a real go/no-go decision.
- Validate before expanding: Confirm performance, policy enforcement, and user experience hold up before rolling out to a second site.
Sequence the Rollout: What Goes First
Once your pilot site is picked, the order you deploy things in depends on what you already have running today, and that's a narrower, more practical question than the single-vendor-versus-dual-vendor decision we can cover. Sequencing gets it wrong more often than you'd expect, usually because it's tempting to build the security layer before the transport layer is confirmed stable, or the reverse.
Your starting point splits into two scenarios: teams that already have an SD-WAN fabric running, and teams building from a flat, traditional WAN. Each one calls for a different first move, and getting that order backward is one of the more common reasons a pilot takes longer than planned.
If You Already Have SD-WAN
For teams with SD-WAN already in place, the practical starting point is layering the security half on top rather than ripping out the transport layer you already paid for. Your existing SD-WAN fabric stays put, since it's already doing its job of connecting sites and prioritizing traffic. What changes is adding cloud-delivered security services, DNS-layer protection, a secure web gateway, and MFA, on top of that connectivity. This is usually the faster path to a working SASE deployment, since you're extending an investment instead of replacing one, and your pilot window can focus on validating the new security layer instead of re-testing connectivity you already trust.
If You're Starting From Scratch
For teams without SD-WAN yet, the case for deploying both halves together from day one is stronger. There's no existing transport layer to preserve, so staggering a SASE implementation, network first, security later, just means running unprotected longer than you need to, without any real benefit in exchange. Deploying both halves in the same pilot window also means your team learns one new management console instead of two, since the SD-WAN and security pieces share the same cloud dashboard. Our guide to Cisco SD-WAN walks through what that networking layer looks like on its own, if you want the deeper technical detail before combining it with the security side.
Cisco-Specific Implementation Options for Multi-Site IT Teams
Everything above applies regardless of vendor, but if you're building on Cisco and Meraki, as most of the multi-site IT teams we work with are, here's what that actually looks like in practice. This is the concrete stack, not the abstract architecture, and it matters because a single-vendor pairing here means one support relationship and one licensing structure instead of stitching together tools from three different vendors.
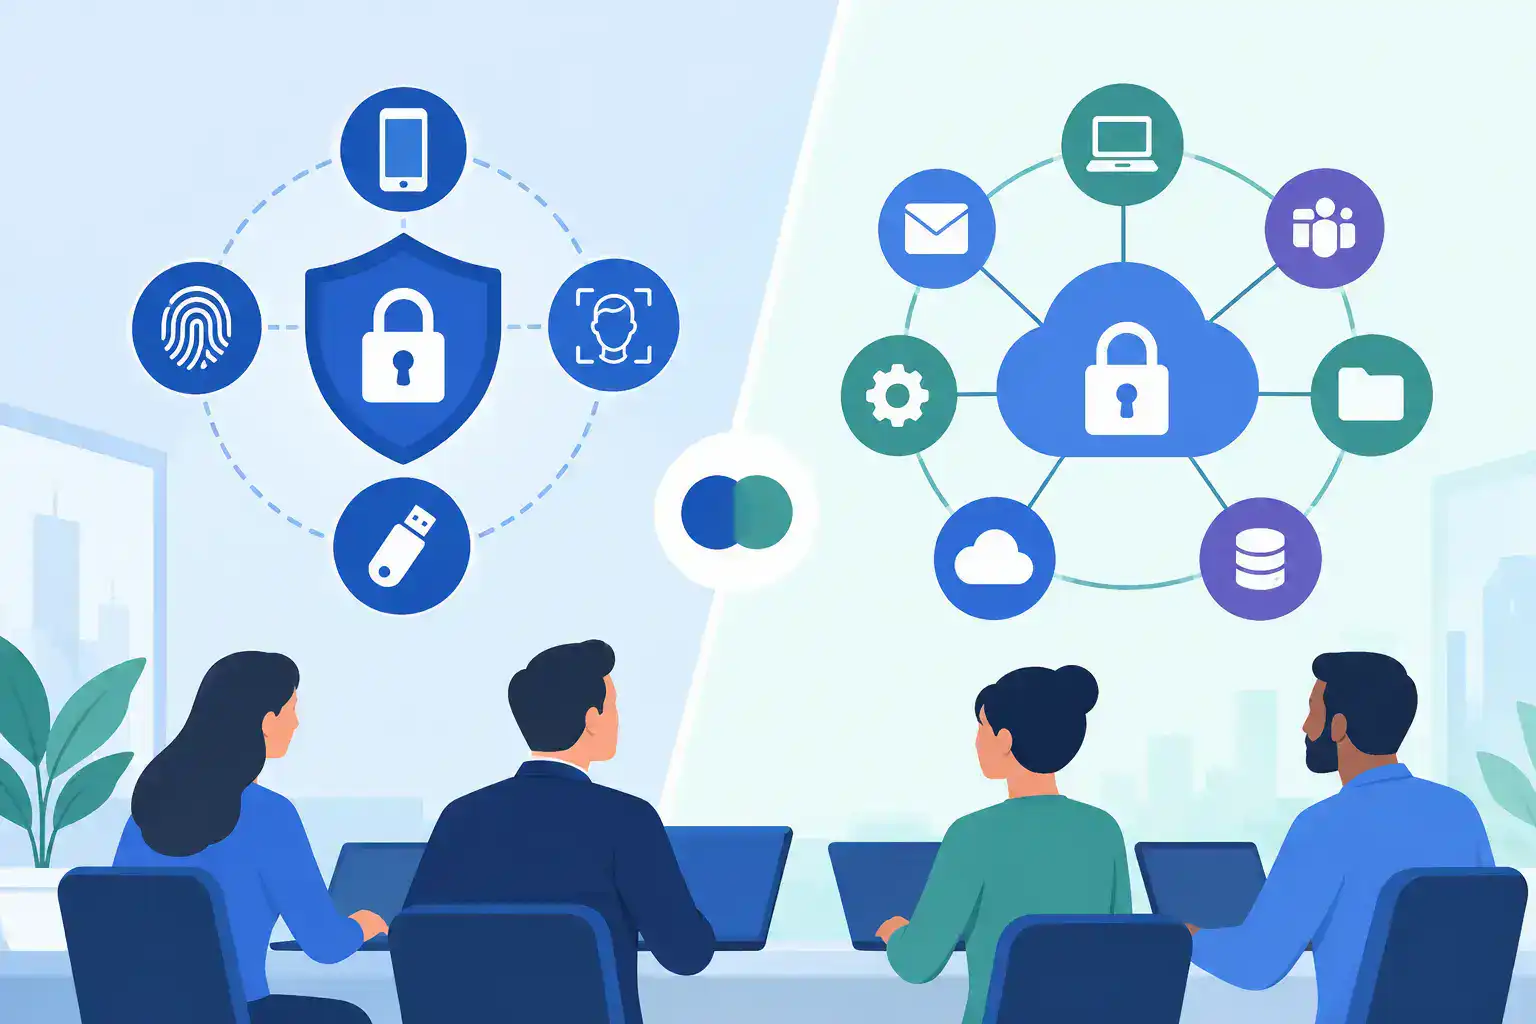
Two pieces do most of the work: Cisco Meraki SD-WAN for the networking layer, and Cisco Secure Access (formerly Cisco Umbrella) paired with Duo for the security layer. Between the two, they cover both halves of a SASE implementation without requiring a separate platform for identity, DNS filtering, or traffic management.
Cisco Meraki SD-WAN for the Networking Layer
Cisco Meraki SD-WAN is built to get multi-site networks online without a heavy on-site lift. New locations connect to the same cloud-managed fabric your existing sites already use, which keeps the networking half of your SASE implementation consistent across every location, whether that's two sites or 20.
- Zero-touch provisioning: New sites come online with minimal on-site IT work.
- Centralized dashboard: Manage every site's SD-WAN configuration from one console.
- Built-in traffic shaping: Prioritize business-critical apps automatically across links.
Cisco Secure Access and Duo for the Security Layer
If you're already on Umbrella, note that Cisco is retiring it on a planned schedule and pointing customers to Secure Access, so this is a forward-looking move rather than a straight rename. Secure Access covers the DNS and web-gateway side; Duo handles identity, so together they close out the security half without a full platform swap.
- DNS-layer security (Cisco Secure Access, DNS Defense): Blocks connections to known malicious destinations before they are made.
- Multi-factor authentication (Duo): Verifies user identity before granting app access, without a heavy deployment lift.
- Combined coverage: Together they cover the secure web gateway and identity-verification pieces of the security half without a full platform swap.
Common Rollout Mistakes That Slow Teams Down
Even with the right stack and a solid pilot plan, most rollouts hit the same avoidable snags. These aren't exotic failure modes specific to SASE. They're the predictable result of skipping a step under deadline pressure, and every one of them is avoidable with a little more patience at the planning stage.
- Migrating every site at once: Skipping the pilot phase means every rollout problem shows up simultaneously, everywhere.
- No rollback plan: Not having a way to revert a site to its previous setup turns a small hiccup into a full outage.
- Skipping end-user communication: Users who aren't told what's changing generate support tickets that look like technical failures but aren't.
- Ignoring failover testing: Confirming failover works in the pilot, not after a live outage, is what actually earns confidence in the new setup.
After Go-Live: What to Monitor in the First 90 Days
Getting through go-live is only half the job. The first 90 days after a SASE deployment tell you whether the pilot's results actually hold up at scale, and it's the window where small issues are still cheap to fix, before they turn into a support ticket backlog or a client-facing outage.
- Latency and uptime: Confirm real-world performance matches what the pilot showed.
- Policy drift: Check that access policies haven't quietly loosened as new users and devices get added.
- Licensing and renewal tracking: Note upcoming renewal dates now, while the deployment details are still fresh.
FAQs
How long does a SASE rollout typically take for a multi-site IT team?
A single-site pilot usually takes a few weeks to run and validate. Full multi-site rollout timelines vary based on how many locations you have and how much of your existing infrastructure carries over, but most teams sequence one site every few weeks once the pilot proves out, rather than rolling out everywhere simultaneously.
Do I need to replace my existing firewalls to implement SASE?
Not necessarily. A phased SASE implementation often keeps your existing firewalls in place at first, layering cloud-delivered security services on top rather than ripping out hardware you've already paid for. Firewalls with a confirmed end-of-sale or end-of-life status are the exception, since those need replacing regardless of your SASE plans.
Can I roll out SASE without an in-house security team?
Yes, with the right partner. Many solo IT administrators run a successful SASE implementation by pairing Cisco's cloud-managed tools with a partner who handles the security-specific configuration and monitoring. You don't need a dedicated security hire to get started. You need a partner who can fill that gap while you handle everything else on your plate.
Want the full picture on networking and security trends shaping SASE?
Download the SASE for Dummies E-Book
Talk to a SASE Deployment Specialist
A SASE implementation plan is only as good as its execution, and execution goes faster with a partner who's done this across more than one site before. If you're ready to move from planning to piloting, or you just want a second opinion on your sequencing before you commit to a timeline, we're here for that conversation.
Contact us for help planning your SASE rollout across Cisco Meraki SD-WAN and Cisco Secure Access